On September 24, cryptocurrency exchange Bitget was hit by a hack. Bitget initially put the loss at $351.6 million, then on September 26 raised the figure to about $387.5 million after tracing additional stolen assets on Zcash and TRON. At that scale, it is the largest reported crypto theft so far this year, surpassing earlier exploits on KelpDAO and Drift Protocol.
How It Happened: No Keys Stolen, the System Approved the Transfers Itself
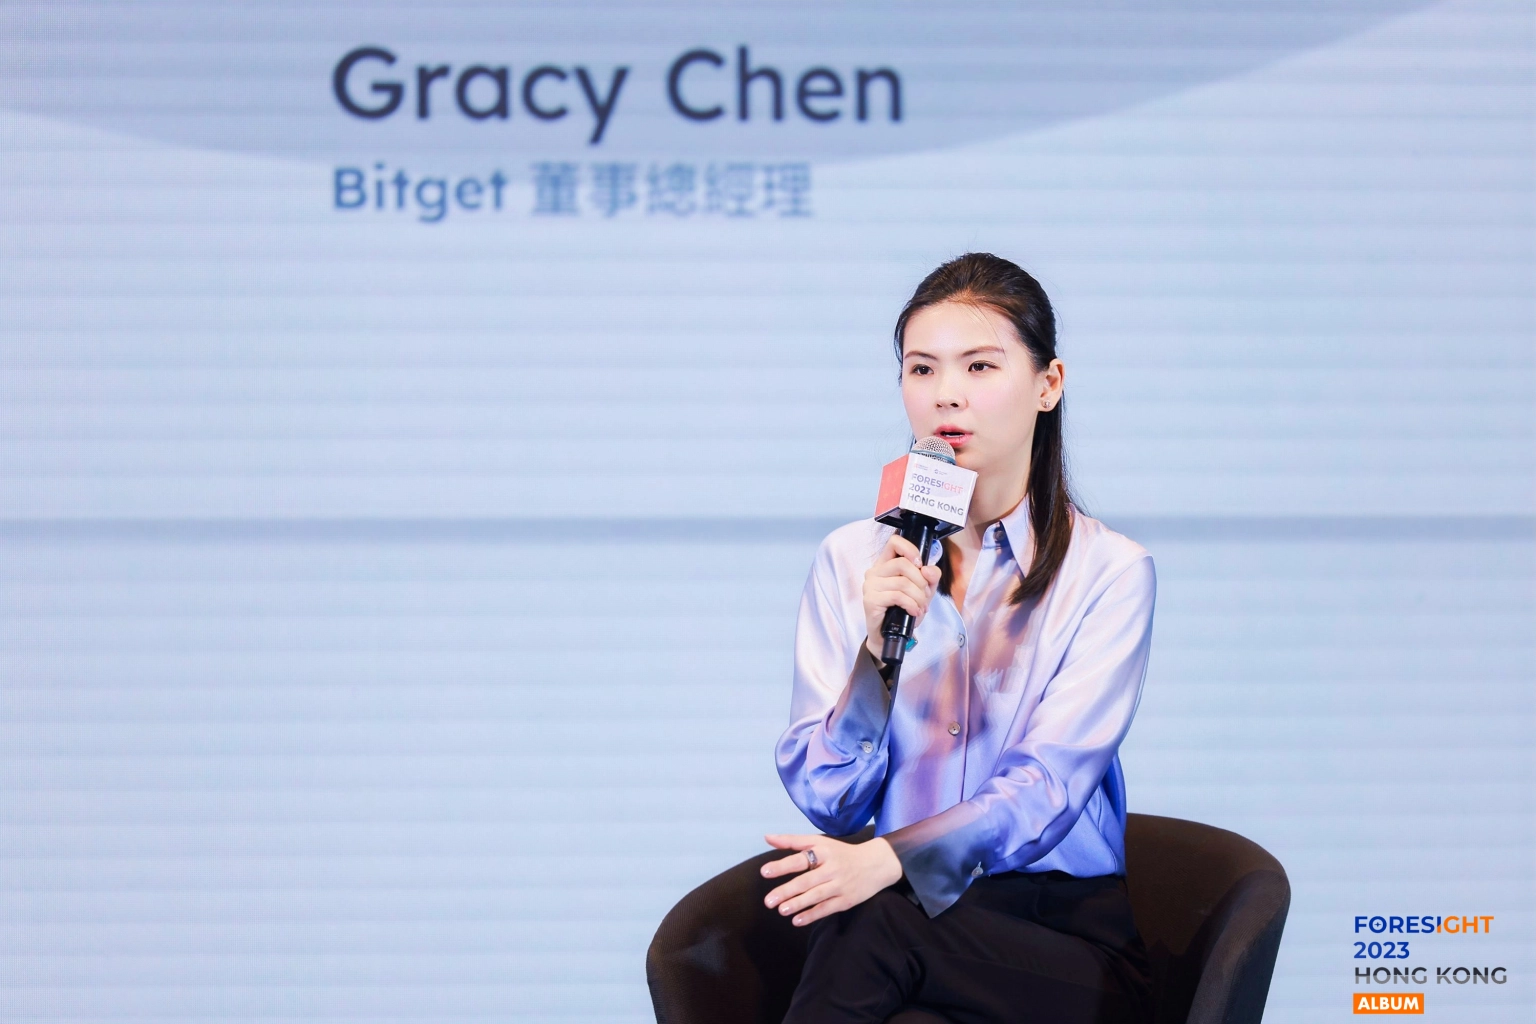
According to Bitget's timeline, its security systems detected unauthorized transfers at 18:31 UTC on September 24 and triggered emergency procedures within minutes. On-chain analysts were already raising alarms: by 21:06, Bubblemaps had observed roughly $180 million moving from Bitget wallets to a single receiving address before being split across multiple wallets. At 21:30, Bitget CEO Gracy Chen publicly confirmed the breach, nearly three hours after the platform's stated detection time.
What sets this attack apart is the method. Gracy Chen said the attackers compromised a critical backend component that manages the wallet infrastructure, fed it falsified transaction data and triggered the platform's own authorization process, while the private keys themselves were never exposed. In a subsequent livestream, Bitget disclosed that the attackers exploited a zero-day vulnerability in a third-party security product to obtain high-privilege internal credentials. They first ran small test transfers, then moved large sums across Ethereum, XRP, BSC, Arbitrum, Avalanche and other chains, and erased their traces afterward. The breach hit parts of the hot and warm wallets, while cold wallets were untouched. The stolen assets included ETH, XRP, BNB, AVAX, USDT, USDC and other tokens, with XRP accounting for the largest single-chain loss.
Bitget's Response: Protection Fund Covers Losses, Withdrawals Resume in Phases
After the incident, Bitget suspended all withdrawals while keeping deposits and trading open. Gracy Chen stated on X that user funds are safe and that the full loss will be covered by the Bitget User Protection Fund, which held more than $464 million at the time. Bitget emphasized that user balances remain intact and brought in Mandiant and SlowMist to conduct an independent investigation.
On remediation, Bitget has isolated the affected systems, reset internal credentials and tightened controls on high-sensitivity permissions and withdrawal verification. Starting September 28, the platform began resuming withdrawals in phases. On asset recovery, Bitget said it will not rely on recovering stolen funds as the primary way to protect users, and launched a bounty program that pays 5% of any amount frozen as a direct result of a party's actions. Circle and Tether froze nearly $318,000 in related stablecoins on September 25.
As for the attackers' identity, Bitget said it will not speculate until the investigation reaches a firm conclusion, but described them as a sophisticated, state-backed group, and had earlier told media it suspects North Korea. On-chain investigator ZachXBT has also linked the stolen funds to North Korea-associated launderers, with activity matching the patterns of the TraderTraitor group.
The Wider Debate: Should Decentralized Protocols Block Stolen Funds?
The incident has also sparked an industry dispute. MistTrack reported that part of the stolen funds appears to have passed through the cross-chain protocol THORChain, which also handled nearly $1.2 billion of the funds stolen from Bybit last year. Gracy Chen publicly asked THORChain to refuse service to the attacker's addresses, warning that the whole industry is watching and that neutrality or decentralization should not be used as cover for letting known stolen funds flow through. THORChain responded that its emergency halt mechanism exists to protect the protocol as a whole and cannot selectively freeze individual addresses. GoPlus Security pushed back on THORChain comparing itself to Bitcoin and Ethereum, pointing to its validator-controlled vaults and documented halt mechanism.
In terms of response, Bitget confirmed the attack on the same day, then disclosed the attack path, remediation steps and a withdrawal resumption schedule, and committed its protection fund to covering the full loss, making its handling relatively transparent. Yet the incident also exposes a new kind of risk facing centralized exchanges: attackers no longer need to steal private keys. By compromising a third-party component and obtaining internal permissions, they can get the platform's own authorization process to wave the transfers through. Third-party component security, internal credential management and cross-chain fund monitoring are becoming essential parts of an exchange's security framework.